How Certification Standards Guide Payment Integration Choices Within Mobile Casino Game Libraries
Quinn Hoffmann · Sep 6, 2026
How Certification Standards Guide Payment Integration Choices Within Mobile Casino Game Libraries
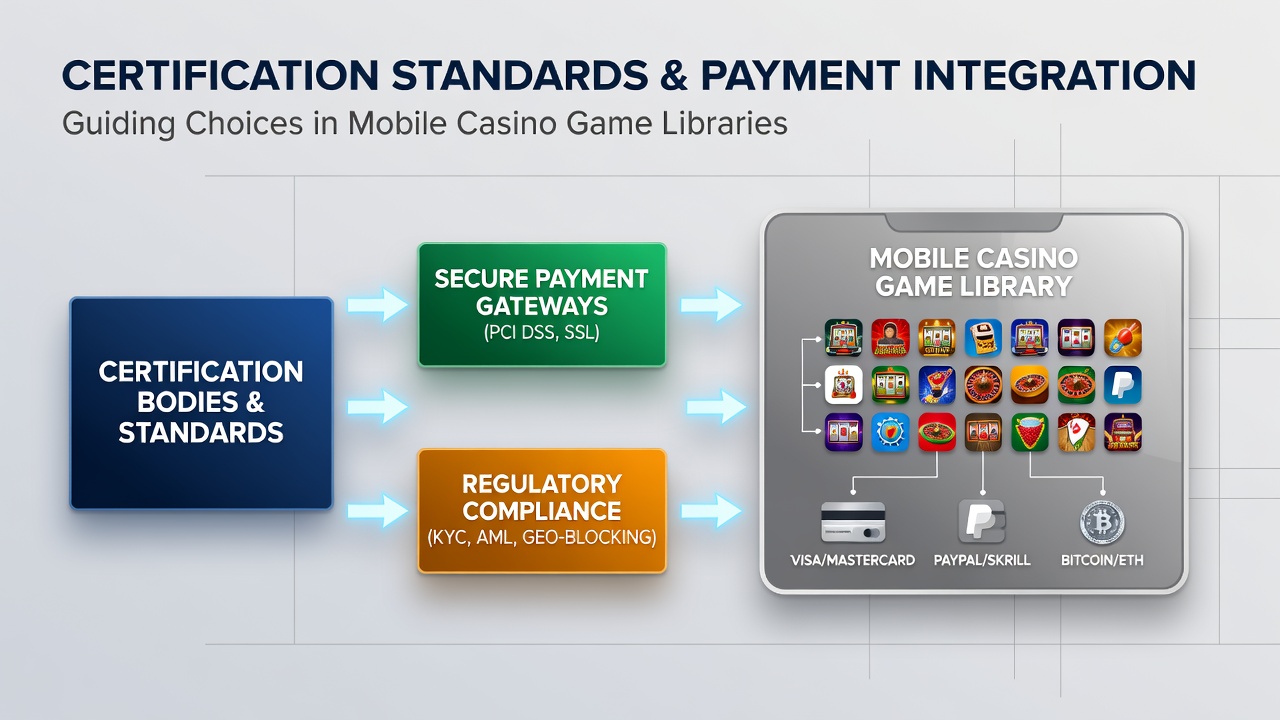
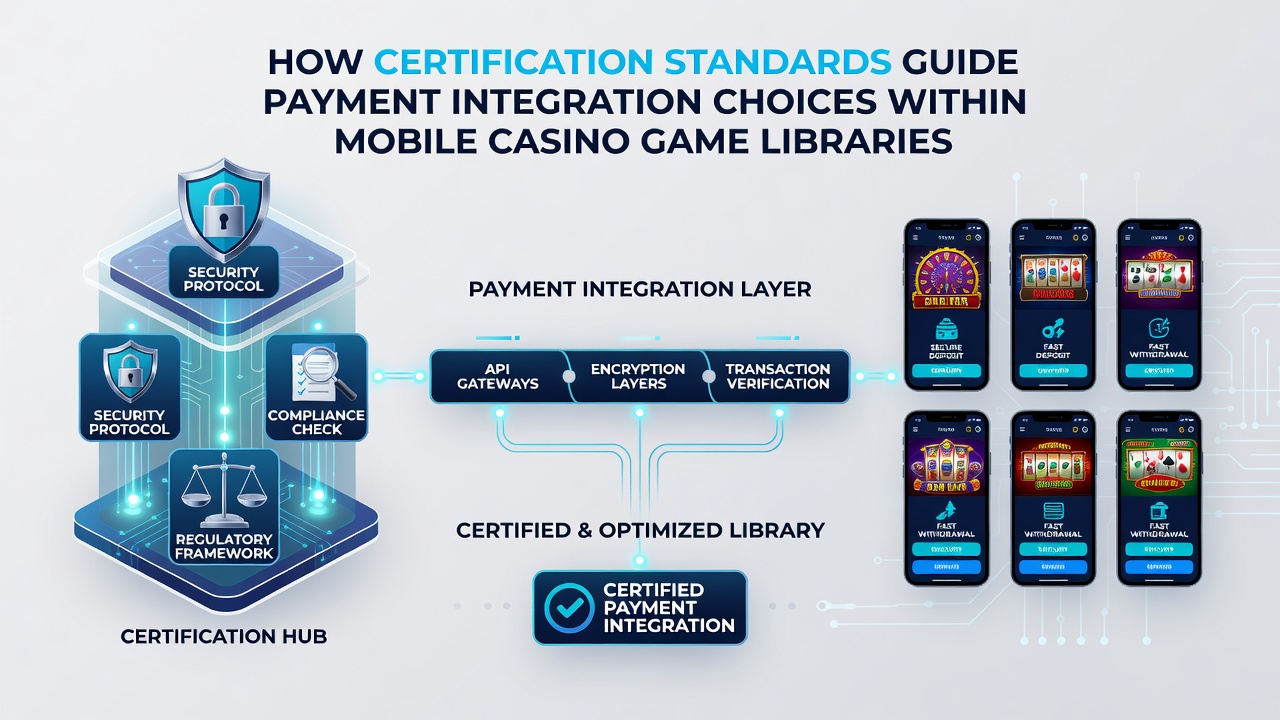
Certification standards shape payment integration in mobile casino game libraries by establishing security protocols, compliance requirements, and interoperability guidelines that developers must follow when connecting to financial networks, and these frameworks determine which processors, encryption methods, and transaction flows gain approval for use across different jurisdictions. Operators select integration pathways based on how well each option aligns with standards such as PCI DSS and regional gaming regulations, while mobile platforms add further layers through app store policies and device-level security certifications that narrow viable choices even before code reaches testing phases.
Core Security Frameworks and Their Influence on Integration Paths
PCI DSS requirements dictate tokenization practices, encryption standards, and data storage limits that directly affect how mobile casino applications handle cardholder information during deposits and withdrawals, and developers therefore prioritize payment gateways already certified at the highest levels to avoid lengthy revalidation cycles. Data from the PCI Security Standards Council shows that organizations maintaining Level 1 compliance experience fewer integration delays when rolling out updates to game libraries, since pre-audited endpoints reduce the scope of each new security review. Those who have studied these patterns note that libraries targeting multiple markets often standardize on processors supporting both PCI DSS and EMVCo specifications, because dual alignment simplifies cross-border transaction routing without duplicating certification efforts.
Regional Regulatory Overlays That Refine Payment Options
Regulators in various regions impose additional certification layers on top of global payment standards, and these rules steer mobile casino providers toward specific integration architectures. In Ontario, for example, the Alcohol and Gaming Commission requires that all payment flows undergo independent testing for responsible gambling controls before they connect to live game libraries, which means developers favor vendors already holding iGaming Ontario certification seals. Similar patterns appear in other jurisdictions where local mandates emphasize audit trails and player fund segregation, prompting libraries to integrate only those processors that publish regular compliance attestations matching the regulator's format.
Mobile-Specific Certification Requirements and Their Impact
App store guidelines from major platforms add another filter to payment integration decisions, because both major ecosystems enforce their own security and privacy certifications that must coexist with gambling-specific standards. Developers therefore evaluate whether a payment SDK carries the necessary attestations for in-app purchases and external wallet connections before committing resources to library-wide implementation. Research indicates that libraries incorporating multiple certified payment rails early in development encounter fewer post-launch revisions, since updates to one standard rarely force complete rewrites when the underlying architecture already meets overlapping criteria.
September 2026 brings scheduled updates to several mobile security frameworks, and observers note that these revisions emphasize enhanced biometric authentication and real-time fraud scoring within certified payment modules. Game libraries preparing for that timeline are already mapping current integrations against draft requirements to minimize disruption once the new versions take effect. One study revealed that providers who maintain continuous compliance monitoring reduce the time needed to adopt revised standards by roughly half compared with those handling certifications only during major releases.
Interoperability Standards and Library Architecture Decisions
Standards bodies focused on gaming technology promote common APIs and data exchange formats that allow payment systems to plug into diverse game libraries without custom bridges for each title. When libraries adopt these interoperability certifications, operators gain flexibility to swap payment providers or add new methods while preserving existing game code, and this modularity becomes especially valuable for studios releasing frequent updates across dozens of titles. Evidence suggests that platforms built around certified interoperability layers report higher rates of successful multi-provider deployments, because the certification process itself weeds out incompatible endpoint configurations before they reach production environments.
Conclusion
Certification standards collectively narrow the range of viable payment integrations for mobile casino game libraries by combining security mandates, regional rules, and platform-specific requirements into a single decision framework. Providers that map their choices against these overlapping certifications from the outset achieve smoother rollouts and fewer compliance-related delays, while those attempting to retrofit integrations after development face repeated validation cycles. The ongoing evolution of these standards continues to guide which payment options appear in live libraries and which remain excluded until they meet the prevailing criteria across all relevant jurisdictions.